
Ireland has been identified as one of five EU countries notably targeted by a Chinese-linked text scam operation, according to a new report from the EU’s cybersecurity agency.
The European Union Agency for Cybersecurity (ENISA) said the Smishing Triad was among the most active cybercrime groups operating across the bloc during 2025, carrying out large-scale campaigns in Ireland, France, Poland, Germany and Lithuania.
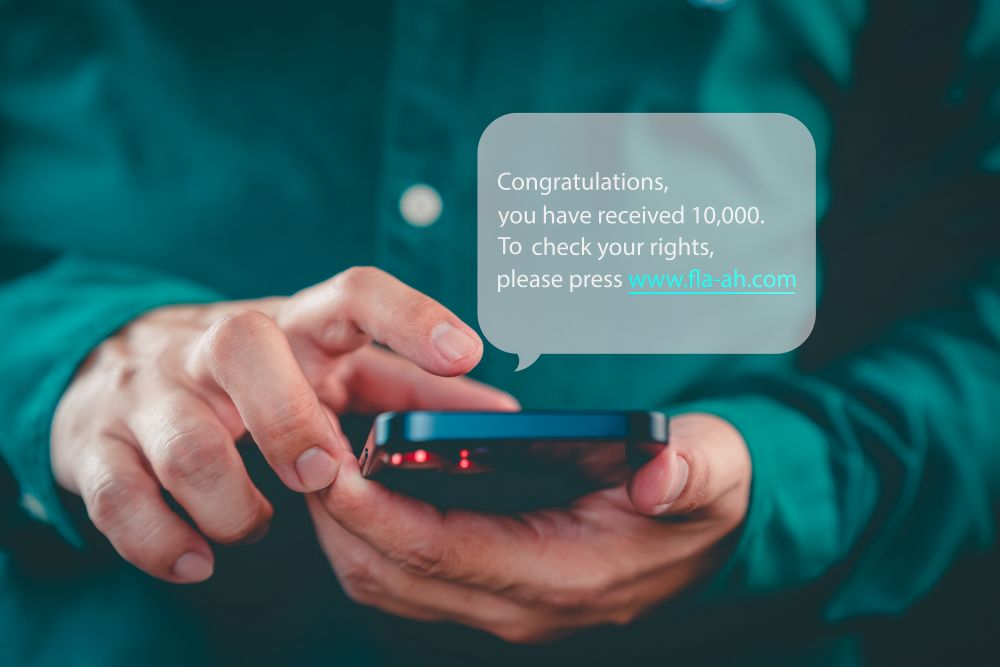
The group uses so-called smishing attacks, in which criminals send fraudulent text messages or messages through mobile apps in an attempt to trick people into revealing sensitive information.
Messages typically impersonate trusted organisations such as banks, delivery companies or government agencies. Recipients are encouraged to follow a link, which can lead to a fraudulent website designed to obtain personal details, banking information or login credentials.
ENISA identified cybercrime as one of the principal cybersecurity threats facing the European Union, with financially motivated attacks accounting for a significant proportion of the incidents recorded during the year.
Ransomware was identified as a particularly serious threat. The agency said ransomware accounted for about 40% of financially motivated cyber incidents, with criminals using malicious software to lock or encrypt computer systems and, in many cases, steal data before demanding payment.
Ireland ranked 11th among 25 EU member states for reported ransomware claims during 2025.
The country was also among just eight EU states to have been targeted by all five of the ransomware groups identified by ENISA as the most active operators in the bloc: Qilin, SafePay, Akira, INC Ransom and Hunters International.
Ireland recorded the fourth-highest level of attacks attributed to the SafePay ransomware group, according to the report.
The threat is particularly significant in Ireland following the devastating ransomware attack on the Health Service Executive in 2021. The attack, attributed to the Russian-linked Conti group, severely disrupted health services across the country.
The HSE has previously estimated that the direct cost of responding to and recovering from the attack was around €100 million, while the State’s auditor has estimated that the overall cost required to address the consequences could reach approximately €660 million.
ENISA also highlighted the continued role of state-linked cyber activity in the European threat landscape.
Russia and China were identified as the countries most frequently associated with state-linked cyber incidents, followed by North Korea and Iran.
According to the report, Russian-linked groups primarily focused their cyberespionage activities on public administration, defence and energy targets across EU member states.
Chinese-linked activity was more heavily concentrated on sectors including telecommunications, maritime industries, semiconductors and manufacturing.
The report also warned about the growing use of information manipulation and interference campaigns.
ENISA recorded 440 detected foreign information manipulation and interference incidents during 2025, highlighting the increasingly broad nature of cyber threats facing EU countries.
The agency's findings underline the range of risks facing Ireland, from mass text-message scams targeting individuals to sophisticated ransomware and state-linked cyber operations targeting organisations and critical infrastructure.